







01
Set Up
your PIMS policies and procedures to meet ISO 27701 requirements
ISO 27701
Achieve and maintain ISO 27701 certification so you can focus on growing your business, customers, and revenue.
Schedule a demo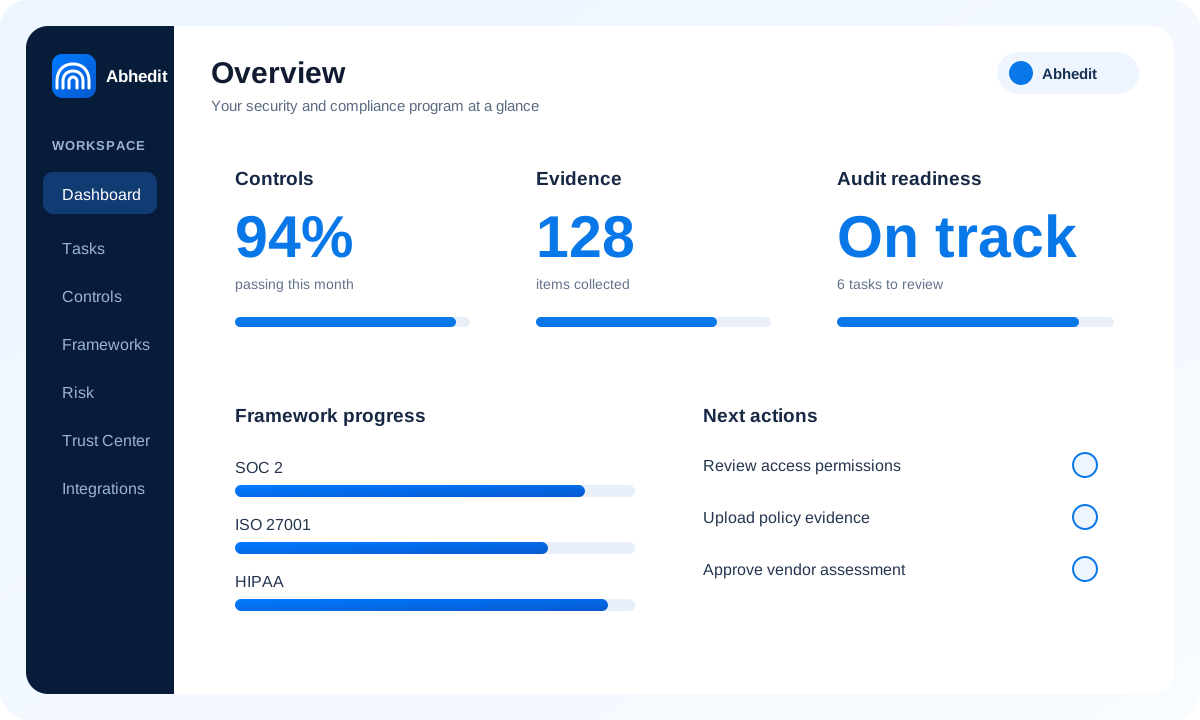
your PIMS policies and procedures to meet ISO 27701 requirements
and monitor your technology stack through our 150+ integrations
your organization’s privacy risks
and maintain your ISO 27701 compliance
Designed for data controllers and data processors, ISO 27701 is an extension of ISO 27001 certification that helps organizations build a Privacy Information Management System (PIMS) to protect personal data and comply with global data privacy standards. ISO 27701 addresses the EU’s General Data Protection Regulation (GDPR) requirements while allowing organizations to incorporate and satisfy other data privacy laws and regulations.
ISO 27701 certification requirements include:
Abhedit’s security and privacy compliance automation platform enables companies to achieve and maintain ISO 27701 certification. We make the compliance process clear by providing procedures and policy templates vetted by ISO 27001 and ISO 27701 experts, proprietary data privacy and security training for automated employee compliance, access to in-house experts, and everything else you need to get compliant.
Design a Privacy Information Management System (PIMS) that aligns with the ISO 27701 standard and your organization’s goals. Select from our library of policy templates, adapt them for your organization, and publish to your employees—all through the Abhedit platform.
Monitor and configure your cloud infrastructure to be ISO 27701 compliant. Plus, no need to install agents — we scan through read-only access.
Complete vendor risk assessments, regularly review vendors, and complete required due diligence.
Ensuring compliance with a strong security and privacy posture means consistently testing your environment. Leverage Abhedit’s pre-built or create custom upload tests for your organization’s unique processes, policies, and controls.